Winning a massive new contract or experiencing a sudden surge in sales is supposed to be a milestone worth celebrating. Unfortunately, for a lot of business owners, rapid growth quickly turns into an operational nightmare. Hardware starts lagging, communication breaks down, and key processes collapse simply because the existing infrastructure was built to support ten employees instead of fifty.
Traditional password rules built around mandatory numbers, special characters, and quarterly resets are officially obsolete. Security standards now prioritize length and usability over artificial complexity, while passwordless alternatives eliminate credentials entirely. Protecting your workstation is a vital duty to safeguard your colleagues and company data.
Most business owners assume their company is too small to attract the attention of an active hacker. Cybercrime has evolved into an automated industry that constantly scans the internet for open vulnerabilities rather than specific brand names. Therefore, leaving your network unsecured effectively guarantees your systems will eventually be found.
When team members bypass IT security guidelines, it is rarely out of malice. In nearly every case, employees are simply trying to get their daily work done without running into digital roadblocks that slow them down. Understanding the reality of security friction is the absolute first step toward fixing it.
Repetitive daily operations and administrative tasks can slow down even the most dedicated workforce, leading to burnout and delayed milestones. Introducing game mechanics into standard business processes provides immediate feedback and clear rewards for routine execution.
When work feels engaging, friction drops significantly.
Most business owners treat technology as a basic utility bill to keep as low as possible. However, sluggish hardware and fragmented tools quietly consume productive employee hours every single day.
Neglecting your infrastructure does not save money; it imposes an unrecorded tax on your overall payroll.
Traditional office perimeters no longer protect modern networks now that many staff members are free to log in from home or local coffee shops. Granting automatic network access based on physical location creates quiet vulnerabilities that bad actors exploit daily.
This is exactly why verifying every identity and endpoint is so essential for anyone in business today: it safeguards your entire organization.
Small businesses miss out on lucrative enterprise contracts every single day, and it rarely has anything to do with the quality of their work. The deal usually grinds to a halt the moment a prospective corporate client hands over a 50-page vendor security questionnaire. Let's talk about how you can prepare your business to pass these audits with confidence.
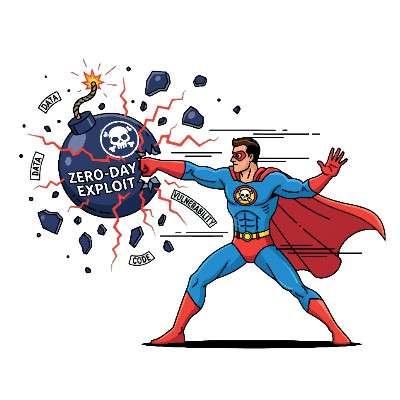
When a massive software vulnerability hits the news…we’re talking about ones that threaten infrastructure, supply chains, or businesses globally…it often feels like an uncontrollable wildfire. The public might panic, but what you don’t see is the quiet, behind-the-scenes work that goes into addressing these issues before they reach your business.
These days, the window of time between a vulnerability being discovered and hackers exploiting it is smaller than ever, and if you wait before taking action, it could cost you your business.
Managing dozens or hundreds of online business accounts requires a realistic security strategy. For years, standard IT policy demanded complex, highly randomized passwords that changed every few months. This approach backfired, leading to recycled password variations and severe security vulnerabilities across organizations.
It is time to discard outdated password rules. Modern password logic focuses on usable security that protects company data without creating operational friction for employees.
Modern cybercriminals have shifted their tactics. Instead of immediately encrypting live production servers, sophisticated attackers now quietly compromise secondary backup archives first; stripping away your ability to restore systems independently. If your enterprise data configurations allow backup logs or files to be altered or deleted, a single breach can permanently destroy your operational records and force costly, catastrophic downtime.
It can feel like every phone call, text message, and email is an attempt to steal money or compromise your network. Scammers target individuals and organizations constantly, using increasingly refined tactics.
While you cannot stop bad actors from sending fraudulent messages, you can implement simple controls to reduce risk. Here are four practical steps you can take to protect yourself and your organization.
A main server hardware failure right before a critical business event can stop operations entirely. In a traditional reactive IT setup, a dead server means waiting days or weeks for new hardware, re-installing applications, and attempting to restore data from manual backups.
With a proactive data resilience strategy, that same hardware failure becomes a minor temporary shift rather than a business disaster.
We all like to think we have a solid handle on our day-to-day operations, but technology has a sneaky way of creating blind spots. Even well-intentioned leaders occasionally fall into simple traps that put their operations at risk. Let’s look at a few of the most easily avoidable IT mistakes and how you can fix them today.
In architecture and engineering, shortcuts often end in spectacular failure. Consider the Tacoma Narrows Bridge: first opened in 1940, engineers had shortened the deck design to save time and weight. The bridge—famously nicknamed "Galloping Gertie"—swayed violently in moderate winds until it ultimately collapsed.
Similarly, in business IT, taking quick shortcuts feels harmless at first, but it creates hidden structural vulnerabilities beneath your day-to-day operations. While cutting corners might save a few minutes today, it routinely compromises long-term security and stability.
Mention complex frameworks like HIPAA, PCI DSS, or data privacy laws, and most managers immediately picture mountains of dry paperwork, confusing audits, and looming fines. It feels like a web of red tape designed for Fortune 500 giants, yet dumped onto small and mid-sized offices that don't have a dedicated legal team on retainer.
When you strip away the legal jargon, IT compliance isn't about pleasing a government bureaucrat or checking boxes for fun. At its core, it's about proving that you take reasonable, standardized steps to protect the sensitive client data trusted to your care.
News & Updates
Contact us
Learn more about what 415 IT can do for your business.
415 IT
1299 4th Street Suite 305
San Rafael, California 94901